// Research
Where cryptography meets implementation.
We study the questions that arise when cryptographic designs meet constrained devices, secure hardware and operational environments.
// In focus
Selected research.
Questions with consequences for implementation, migration and trust.
Toward an open cryptographic workbench.
Cryptographic tools explain algorithms, transform data and visualise workflows. A protocol workbench could connect those strengths while keeping exact bytes visible.

What post-quantum migration costs at the edge.
Post-quantum algorithms change the size and shape of protocols. At the edge, bytes, memory, latency and update paths become part of the cryptographic decision.
// Research archive
Latest research.
Primers, analysis and reviews, with series and article type made explicit.

The other three questions.
Most cryptography education for children begins and ends with confidentiality. Integrity, authentication and credentials can be modelled with simple roles and objects, even as age-assurance systems make those properties part…

Cryptography can start before algebra.
Children can learn the questions cryptography answers before they can learn the mathematics behind its algorithms. Existing school materials teach secrecy well, but leave integrity, authentication, identity and trust comparatively…

Seven containers, ranked by what you can prove.
Mobile key containers form a degradation ladder ordered by what an issuer can prove, not only by resistance to attack. Below the policy cut line, fallback changes the custody model…

The certificate has two lists.
Android key attestation records a key's security level and separates authorizations enforced by hardware from those enforced by software. A verifier must validate the certificate chain, revocation status, boot state…

What “hardware-backed” means on Android.
Android exposes software, TEE-backed and StrongBox-backed keys through one keystore API. The effective security level, mandated algorithm set and available attestation evidence vary by device and release.

Colour buys capacity in exchange for illumination.
Polychrome barcodes can multiply payload density, but they exchange binary contrast for dependence on inks, cameras and uncontrolled light.

What survives the print, the scan and the phone.
Error correction can recover exact codewords from a damaged symbol. It cannot recover biometric detail removed before the credential was printed.

A face fits in 960 bytes.
A signed QR can carry an offline face credential, but signature, encoding and card geometry leave roughly one kilobyte for the image.
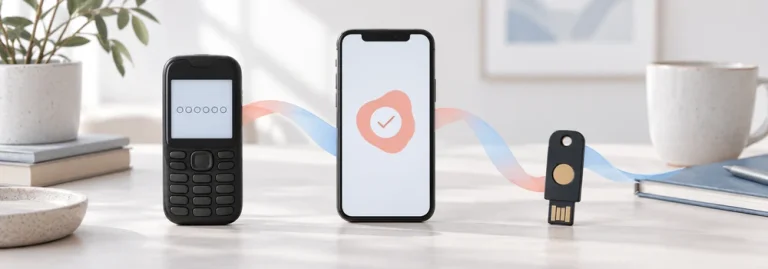
SMS OTP is now a restricted authenticator. The hard part is what replaces it.
Leaving SMS removes the telephony channel, but phishing resistance depends on origin binding and on every recovery path that can create a session.

Six digits are not the authentication ceremony.
An OTP output is short and temporary. Its real security depends on seed custody, moving-factor state, verification policy, session binding and recovery.

The verifier and the parser disagree.
Signature verification fails as a security boundary when the verifier and the application resolve different meanings from the same document.

Signatures are over bytes, not meaning.
Two messages can express the same data and still produce different signatures. Verification begins with the exact bytes a protocol chooses to protect.

Audit the attributes, not the datasheet.
PKCS #11 key policy is expressed through attributes and mechanisms inside the token. An inventory can reveal permissions that a product datasheet cannot.

The handle is not the key.
PKCS #11 gives applications a common view of cryptographic devices. The key's policy, lifecycle and operational meaning still depend on what lies behind the handle.

Entropy arrives late.
Correct algorithms can still generate related keys when identical devices ask for randomness before their environments have diverged.

Twenty-six years from break to scheduled retirement.
SHA-1's long retirement measures inventory, artifact lifetime and the unreachable tail of deployed systems more than cryptanalysis.

The handshake has a budget of fourteen kilobytes.
Post-quantum authentication can cross transport limits before application data begins. The real budget is measured in bytes, flights, fragments and buffers.

A random output can carry a proof.
A verifiable random function produces a unique, random-looking output and evidence anyone can check. It proves origin and uniqueness, not fairness in deciding which outputs are revealed.

Removing a member creates a new epoch.
Messaging Layer Security makes membership part of shared cryptographic state. A removal takes effect when the remaining group commits and derives a new epoch.

The ciphertext does not say which mode produced it.
Format-preserving ciphertext carries no mode, key or tweak metadata. That convenience makes FF1 and FF3 migration difficult to scope from the data alone.

Preserving the format preserves the leakage.
Format-preserving encryption keeps ciphertext compatible with narrow legacy fields. It also keeps domain size, length, structure and often equality visible.

A compact handshake still has a transcript.
EDHOC compresses authenticated key exchange into three concise CBOR messages. Its efficiency still depends on exact transcript bytes, credential profiles and state transitions.

Two key exchanges still make one protocol.
A hybrid key exchange combines a traditional contribution with a post-quantum one. Its guarantee depends on the combiner, transcript, negotiation and every failure path around both components.

Sign the same message twice.
Repeated signing reveals whether output varies. Across a population, repeated ECDSA values can expose nonce reuse, compromise and implementation anomalies.

Determinism is not a substitute for entropy.
Deterministic signing prevents catastrophic dependence on fresh random nonces. Hedged signatures add new randomness to reduce repeated traces and faults without trusting that randomness completely.

No intermediary should see the whole request.
Oblivious HTTP partitions network identity and request contents between a relay and a gateway. Padding, discovery, metadata and collusion still determine the privacy of the complete system.

Evidence is not a verdict.
Remote attestation authenticates evidence about a target environment. Endorsements, reference values and appraisal policy are what turn that evidence into a decision.

A key directory should be accountable.
Key transparency gives public-key distribution a consistent, auditable history. Its proofs expose silent substitution only when clients, monitors or witnesses compare committed views.
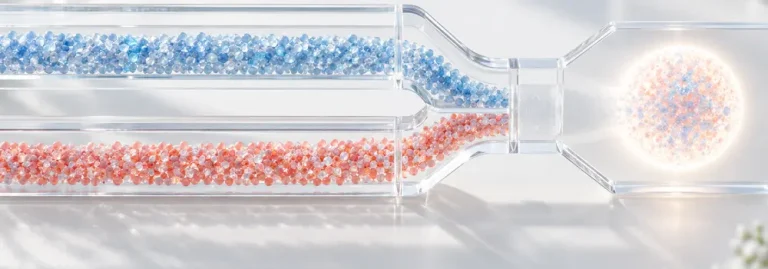
The aggregate can be known without collecting each value.
VDAFs let several aggregators verify and combine hidden client measurements. The result protects individual values only when non-collusion, batching and query policy hold.

Authorization does not require identity.
Privacy Pass separates token issuance from token redemption. The token can prove prior authorization without carrying a stable client identity.

The server does not need the password.
OPAQUE lets a client and server establish a mutually authenticated key without disclosing the password to the server. Registration, recovery and server-key custody still define the system's real boundary.

The signature is ordinary. The ceremony is not.
FROST turns distributed authority into one ordinary Schnorr signature. The difficult security work remains in share generation, nonce state, participant coordination and recovery.

The statement must enter the hash.
A zero-knowledge proof can verify correctly while authorizing the wrong statement. Fiat-Shamir security begins with the exact public instance, transcript order and domain separation absorbed by the hash.
Selective disclosure is not unlinkability.
BBS signatures support selective disclosure and randomized derived proofs. Unlinkability still depends on disclosed values, proof context, revocation and the surrounding protocol.
A blockchain can preserve a claim. It cannot make it true.
Hashes, signatures and consensus can preserve an ordered claim. They cannot establish the external truth, authority or intent behind it.
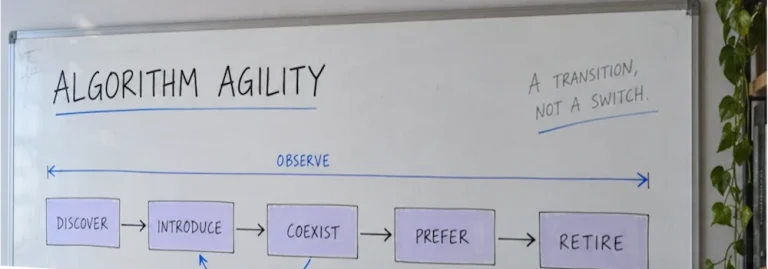
Algorithm agility is an operational property.
Supporting a second algorithm is easy. Moving a running system from one cryptographic regime to another is the real test of agility.
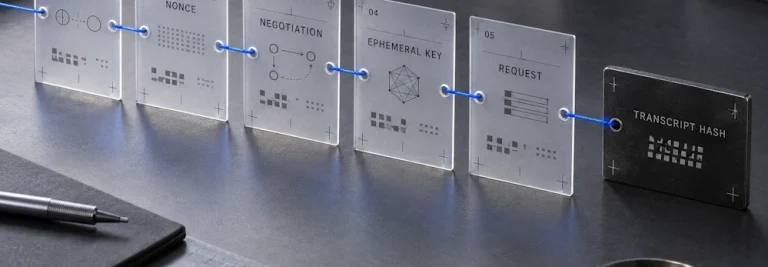
The transcript is the protocol.
A secure session depends on more than fresh keys. The negotiation, participants and intended operation must be bound to the same cryptographic result.

A nonce is not a footnote.
A secure cipher can fail when nonce state does not survive writers, restarts and rollbacks. Uniqueness is a property of the operating system around the primitive.

The curve is only part of the choice.
P-256, secp256k1, Ed25519 and X25519 name different layers, purposes and ecosystems. Selecting a curve never selects the complete construction.